Cross-border SAP and Personal Data Technical Path
Cross-border SAP and Personal Data Technical Path
Cross-border SAP and personal data technical path: data classification, topology options and a control checklist for counsel review.
This is not legal advice. This case describes a technical and process path only. Legal counsel owns all legal opinions and final decisions; Easyton does not provide legal or compliance services and does not certify PIPL, GDPR or any other regulatory compliance.
Project context
- Setting: Multinational SAP landscape touching China and overseas
- Scale: Manufacturing / trading with SAP
Challenge
A multinational SAP deployment needed a coherent discussion of where systems run, what personal data classes flow, and which cross-border path options exist (localization, gated transfer, minimization). The client’s legal counsel owns all legal opinions; Easyton’s role was limited to technical architecture options and documentation.
Environment
- SAP ECC/S4 (as applicable) with integrations
- HR/customer personal data potentially in scope
- China egress controls and corporate global templates may conflict
- Multiple vendors (SAP basis, network, cloud)
Solution architecture
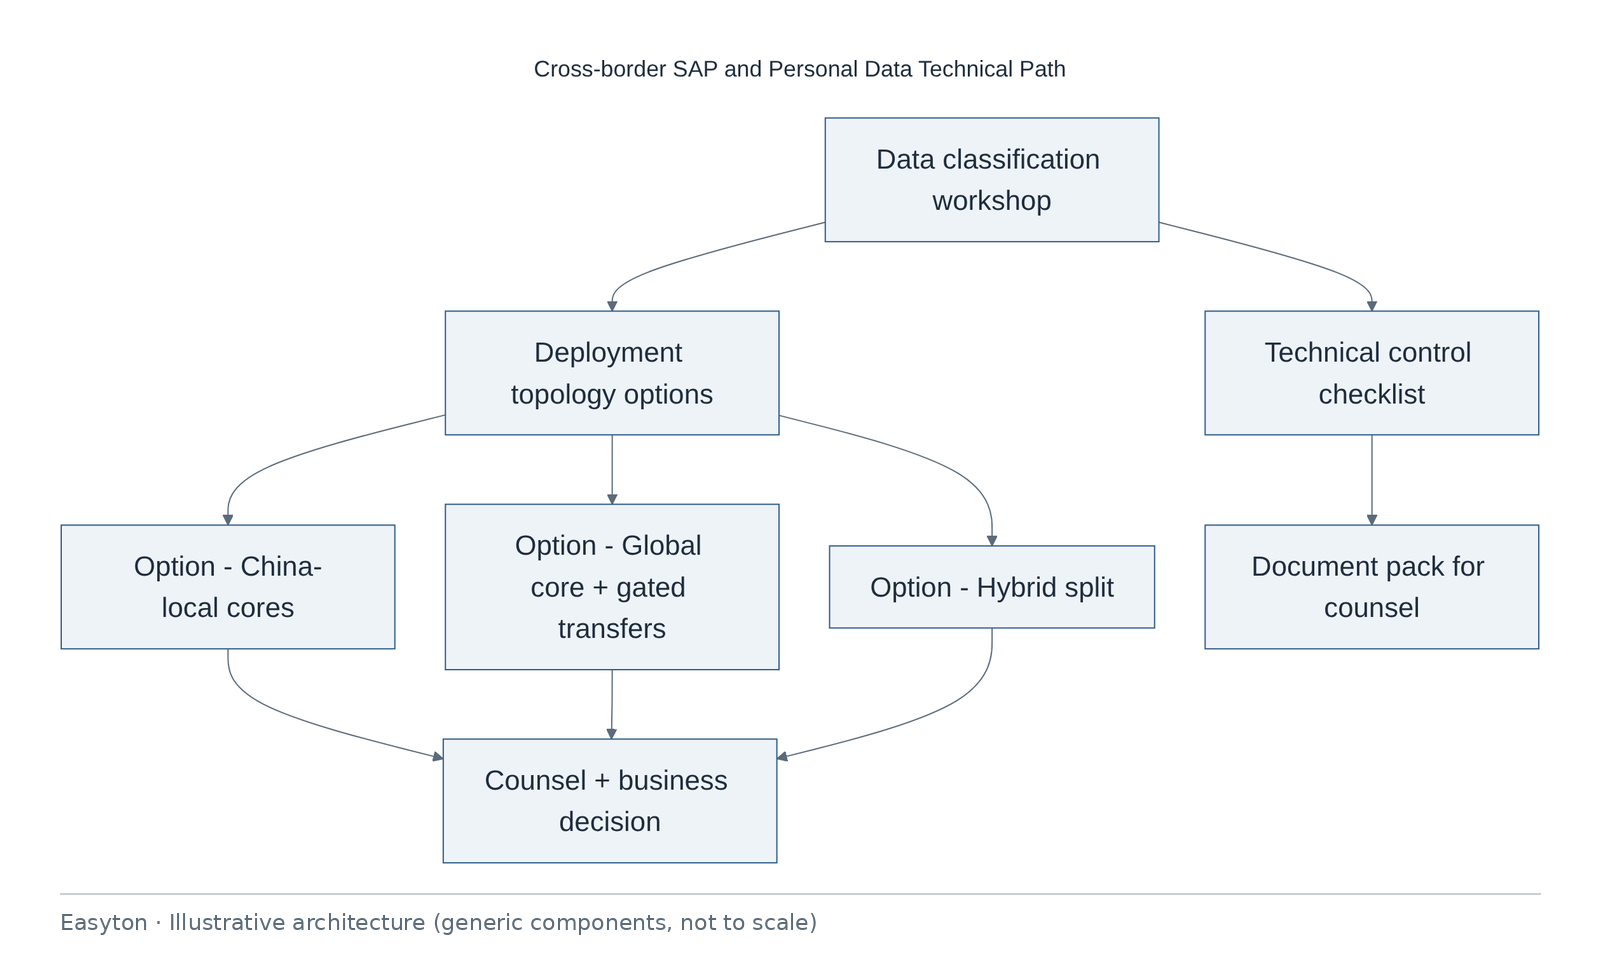
Text view of the architecture (each line: component → what it connects to):
Data classification workshop → Deployment topology options, Technical control checklist
Deployment topology options → Option - China-local cores, Option - Global core + gated transfers, Option - Hybrid split
Technical control checklist → Document pack for counsel
Option - China-local cores → Counsel + business decision
Option - Global core + gated transfers → Counsel + business decision
Option - Hybrid split → Counsel + business decision
Technical highlights
Topology options (illustrative)
- Describe patterns without asserting which law “requires” which pattern.
- Network paths: private line / IPSec / cloud interconnect—implementation detail in SOW.
Data classification
- Categories: HR · customer · vendor · telemetry · none
- Minimization and retention themes; the data inventory is treated as a working document, not a certified record.
Technical control checklist (examples of types)
- Access IAM · encryption in transit · logging · DLP patterns · admin bastion · interface allow-lists · anonymization/pseudonymization where designed
Document pack for counsel
- Data-flow abstracts · system inventories · control matrices · open questions list
- Explicit cover sheet: “For legal review — not a compliance certificate.”
What Easyton does not do
- Promise approval by regulators
- Quote unpublished legal interpretations as fact
- Invent transfer impact assessment scores
Implementation steps
- Kickoff with client counsel
- Classification workshop
- Topology options memo
- Control checklist draft
- Document pack
- Client counsel review
- Implement approved technical SOW separately
Acceptance
- Options memo delivered
- Classification workshop minutes exist
- Control checklist versioned
- Cover disclaimer present
- Counsel acknowledgement of receipt (receipt only)
Deliverables
- Topology options memo
- Classification worksheets
- Technical control checklist
- Counsel document pack
- Open questions register
Outcome
Technical deployment options and control documentation were prepared to support decisions led by the client’s own legal counsel.
This is not legal advice. This case describes a technical and process path only. Legal counsel owns all legal opinions and final decisions; Easyton does not provide legal or compliance services and does not certify PIPL, GDPR or any other regulatory compliance.
Related
Easyton has delivered IT infrastructure and support projects since 2009. Planning something similar? Contact Easyton to discuss your requirements.